Why Your Site Says 'Not Secure' (4 Fixes)

Every browser now passes judgment on your site before a visitor reads a single word. Chrome prints Not Secure next to your address, Safari warns the connection is not private, and on a phone the warning fills the screen with a scary full-page interstitial. Visitors do not parse the technical details; they see a warning next to your business name and hit back. The cause is almost always one missing or misconfigured certificate, and the fix is usually free and done in under an hour. This guide walks the four fixes in order of likelihood, with a check to confirm each one worked.
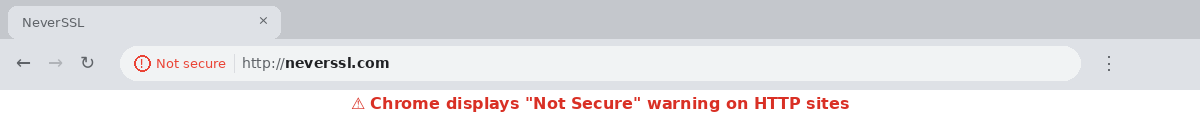
A visitor types in your address, your site loads, and before they read a single headline the browser tells them not to trust you. "Not Secure", right there in the address bar. Chrome has shown that label on every plain HTTP page since version 68 shipped in July 2018, and Safari, Edge, and Firefox all do a version of the same thing.
Here is the part most guides skip: the warning almost never means you were hacked. It means the connection between your visitor's browser and your site is not encrypted, so anything they type (a contact form, an email address, a password) travels as readable text. Browsers punish that, and so does Google, which has used HTTPS as a ranking signal since 2014.
The good news is that there are only four common causes, and they are easy to tell apart. Work through them in order. Most sites are fixed at step 1 or step 4.
What the warning looks like (and what the fix looks like)
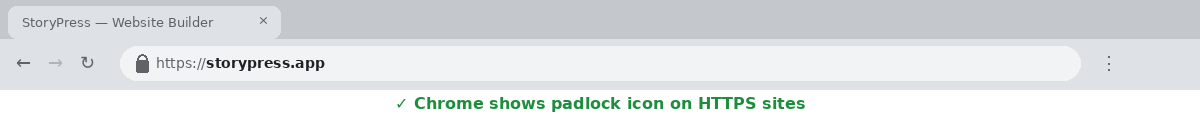
Here is the difference between an HTTP site and an HTTPS site in Chrome's address bar.
Step 1: Install a certificate (if you have none)
An SSL/TLS certificate is what lets your site speak HTTPS. Fifteen years ago these cost real money. Today they are free through Let's Encrypt, a nonprofit certificate authority that issues certificates for hundreds of millions of websites.
How to verify: open your site in a private browsing window and check the address bar shows https:// with no warning. Then paste your domain into the free Qualys SSL Labs test. Anything graded B or above means the certificate itself is fine.
Step 2: Renew an expired certificate
Certificates have a shelf life. Let's Encrypt certificates last 90 days and are meant to renew automatically. When you see "certificate expired", the renewal robot at your host has stalled.
How to verify: click the padlock, open certificate details, and confirm the "valid until" date is in the future. Set a calendar reminder 2 weeks before it, once, to confirm auto-renewal actually worked the first time.
Step 3: Fix a domain mismatch
A certificate is issued for specific names. If it covers yourdomain.com but a visitor arrives at www.yourdomain.com (or the other way round), the browser treats it as the wrong ID and shows a full-page warning.
How to verify: type all four variants into the browser (http://, https://, with and without www). All four should land on the same secure address with no warnings.
Step 4: Clear mixed content (the sneaky one)
This is the case where you already installed a certificate, the padlock should be there, and the browser still says the page is not fully secure. The cause is almost always mixed content: your page loads over HTTPS but one or more things on it (an image, a font, a script, an embedded widget) still loads over plain HTTP.
Google's developer team keeps a thorough reference on this in Fixing mixed content if you hit an unusual case.
How to verify: reload the page with the Console open. No mixed content lines and a clean padlock means you are done.
The padlock is not a technical detail. It is the first trust decision a visitor makes about your business, and it happens before they read a single word.
Or skip the whole checklist
Everything above assumes you are running your own hosting stack, because that is where these problems live. Modern managed platforms handle it for you: every StoryPress site ships with HTTPS on from day one, certificates that renew themselves, and no plugin or panel setting that can silently expire. If you would rather never think about padlocks again, that is the simplest fix of all.
Either way, do the SSL Labs check today. It takes two minutes, and "Not Secure" is the one website problem where every single visitor sees the damage.